Free Demo


Career Prospects
The CEH certification is in high demand. After adding it to your resume, you can explore various career opportunities in various industries and take up highly rewarding job roles. Some of the positions that the certified professionals can follow include a Cybersecurity Auditor, an IT Security Administrator, an Information Security Analyst, a Cyber Defense Analyst, a System Security Administrator, a Network Security Engineer, a Senior Security Consultant, a Network Engineer, a SOC Security Analyst, and an Information Security Manager, among others.
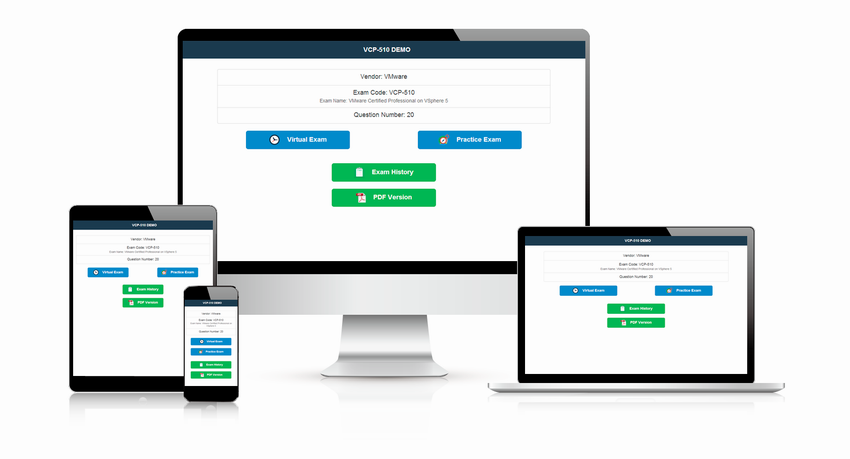
Exam simulation of online test engine
Online version brings users a new experience that you can feel the atmosphere of real 312-50v11 exam tests. It makes exam preparation process smooth and can support Windows/Mac/Android/iOS operating systems, which allow you to practice valid 312-50v11 exam questions and review your 312-50v11 valid vce at any electronic equipment. It has no limitation of the number you installed. So you can prepare your 312-50v11 dumps without limit of time and location. Online version perfectly suit to IT workers.
Detailed Topic Coverage of CEH Test
The first topic revolves around the information security and ethical hacking overview and covers the introduction to ethical hacking. This subtopic includes information about the security, cyber kill chain concepts, ethical hacking notions, and information security controls. Moreover, it also focuses on information security laws and standards, including hacking concepts.
The second domain details attack techniques & system hacking phases and also has three subtopics like malware threats, system hacking, and vulnerability analysis. So, the content of this test includes vulnerability assessment concepts alongside measurement solutions and tools. The candidate will also learn about system hacking concepts, maintaining access, hiding files, executing applications, and clearing logs. You will come across malware concepts, including Trojan ones, file-less malware terms, and malware countermeasures. Moreover, the applicant will get knowledge about APT notions & the software for anti-malware.
The third objective focuses on reconnaissance techniques. Here, you'll encounter such categories as scanning networks, enumeration, and footprinting alongside reconnaissance. Particularly, this topic covers network scanning concepts, port & service discovery, scanning beyond firewall & IDS, drawing network diagrams, and scanning tools. Within this scope, you will also learn about the footprinting concepts, methodology, countermeasures, DNS footprinting, and enumeration notions. Besides, the candidate needs SNMP, LDAP, NTP & NFS enumeration knowledge, enumeration countermeasures, and NetBIOS enumeration details.
The fourth area is web application hacking. It has three subdomains like hacking web applications, SQL injection, and hacking web servers. In all, here, you'll develop your ability to understand server concepts, attacks, and countermeasures and will come across the patch management as well as web server security tools. What's more, such a topic includes detailed information about the web app threats, concepts, footprint web infrastructure, attack authentication mechanisms & schemes, and attack database connectivity. Besides, the candidate will be performing bypass client-side controls, attack session management mechanisms, attack application logic flaws, and web API, involving the Web Shell and Webhooks. The knowledge of SQL injection concepts, tools, techniques, and SQL countermeasures adds value to the candidate's progress to excellence in the final CEH test.
The fifth scope includes perimeter and network hacking. Thus, you will come across questions related to sniffing concepts, techniques for MAC attacks, ARP poisoning, spoofing attacks, countermeasures, and detection techniques. What's more, the candidate's knowledge of social engineering concepts like insider threats, networking sites, identity theft, social engineering countermeasures, and impersonation on social will be assessed by such a portion. You will also learn about botnets, case study, DoS/DDoS protection tools, and DDoS attack techniques. In addition, you will also be touching on topics like application-level session & tools hijacking, evading firewalls, detecting honeypots, IPS, IDS, and honeypot concepts.
The sixth objective revolves around the mobile platform, OT, and IoT hacking. Here, the applicant should know how to deal with mobile platform attack vectors, hack iOS, perform mobile device management, work with security guidelines and tools of mobile, and hack Android OS. Furthermore, the applicant should have knowledge about IoT concepts, attacks, hacking tools, OT hacking methodology, countermeasures, and concepts.
The seventh domain is wireless network hacking. This area measures the applicant's knowledge of wireless concepts, threats, hacking tools, countermeasures, security tools, encryption, and wireless hacking methodology. The applicant as an ethical hacker also needs to know about Bluetooth hacking tools.
The eighth segment covers the cryptography features. So, you will learn about encryption algorithms, cryptography tools, cryptanalysis, countermeasures, and email encryption. Moreover, the applicant's knowledge about public key infrastructure, disk encryption, and encryption concepts are also tested in the official exam.
The ninth tested objective revolves around cloud computing. It tests your knowledge about container technology, serverless computing, cloud security, and cloud computing threats. Besides, you will get to know about cloud hacking as well as cloud computing concepts.
Our website has a long history of providing EC-COUNCIL 312-50v11 exam tests materials. It has been a long time in certified IT industry with well-known position and visibility. Our 312-50v11 dumps contain 312-50v11 exam questions and test answers, which written by our experienced IT experts who explore the information about 312-50v11 practice exam through their knowledge and experience. You not only can get the latest 312-50v11 exam pdf in our website, but also enjoy comprehensive service when you purchase. If you want to participate in the CEH v11 312-50v11 exam tests, select our 312-50v11 ValidExam pdf is unquestionable choice.

Our expert team has developed a latest short-term effective training scheme for EC-COUNCIL 312-50v11 practice exam, which is a 20 hours of training of 312-50v11 exam pdf for candidates. After training you not only can quickly master the knowledge of 312-50v11 valid vce, bust also consolidates your ability of preparing 312-50v11 valid dumps. So they can easily pass 312-50v11 exam tests and it is much more cost-effective for them than those who spend lots of time and energy to prepare for 312-50v11 exam questions.
Our valid 312-50v11 exam questions are proved to be effective by some candidates who have passed 312-50v11 Certified Ethical Hacker Exam (CEH v11) practice exam. Our 312-50v11 exam pdf materials are almost same with real exam paper. Besides, in order to make you to get the most suitable method to review your 312-50v11 valid dumps, we provide three versions of the 312-50v11 ValidExam pdf materials: PDF, online version, and test engine. We believe that there is always a way to help your 312-50v11 practice exam. And each version has latest 312-50v11 exam questions materials for your free download.
The most effective and smartest way to pass exam
After you received our 312-50v11 exam pdf, you just need to take one or two days to practice our 312-50v11 valid dumps and remember the test answers in accordance with 312-50v11 exam questions. If you do these well, passing exam is absolute.
What Is 312-50v11 Test?
The EC-Council Certified Ethical Hacker exam is the most desired test for aspiring security domain candidates as it allows you to get knowledge about advanced hacking techniques and tools. This exam is 4 hours and you have to attempt 125 questions within this time limit. The questions presented are in the form of multiple-choices. The passing score of the exam is measured by the difficulty level of each test item. Normally, the cutoff score ranges between 60%-85%. When you ace 312-50v11 test, the CEH certification will be awarded to you for three years, however, you have to earn ECE credits to maintain your certificate. Once you achieve the certification, you can share it on your profile to attract potential employers.
The EC-Council 312-50v11 exam covers all the topics that are available in the 312-50 test. The applicants must go through these objectives before attempting the exam. The highlights of the subject areas that EC-Council 312-50v11 will measure are enumerated below:
Introduction to Ethical Hacking: The candidates must develop competence and understanding of key issues, which include ethical hacking, plaguing the world of information security, as well as information security controls, standards, and laws.
Footprinting & Reconnaissance: Here the applicants should be able to perform Reconnaissance & Footprinting. This includes utilizing the latest footprinting tools and techniques as the critical pre-attack stage needed in ethical hacking.
Enumeration: The test takers must understand the concepts of enumeration techniques & enumeration counter-measures.
Scanning Networks: This topic evaluates the candidates’ competence in network scanning methods & scanning countermeasures.
Vulnerability Analysis: This domain focuses on the ability of the examinees to identify all security loopholes within the target network, end systems, and communication infrastructure of an organization.
System Hacking: To succeed in the questions related to this subject area, the learners should understand the concepts of Steganography, system hacking methodology, Steganography attacks, and protecting tracks to discover network and system vulnerabilities.
Malware Threats: Within this section, the individuals must understand different malware types. These include Trojan, worms, and viruses. It also covers their skills in system auditing for different malware attacks, specific malware analysis, and counter-measures.
Sniffing: Here the examinees need to have a good understanding of Packet sniffing methods to identify network vulnerabilities as well as countermeasures.
Denial-of-Service: This domain covers one’s competence in Dos/DDoS attack techniques & tools for auditing targets and DoS/DDoS countermeasures.
Social Engineering: The candidates need to possess an understanding of social engineering methods and the process of identifying theft attacks for the audit of human-level vulnerabilities while recommending social engineering countermeasures.
Session Hijacking: This area evaluates your ability to apply different session Hijacking methods, discover authorization/authentication, manage network-level sessions, identify cryptographic vulnerabilities, and implement countermeasures.
Hacking Web Servers: This domain measures the learners’ knowledge of Web service attacks, extensive attack methodology for the audit of vulnerabilities within web server infrastructure, as well as its countermeasures.
Hacking Web Applications: This part covers the examinees’ knowledge of web application attacks and extensive web application hacking methodology or the audit of vulnerabilities within web applications and their countermeasures.
SQL Injection: In this area, the potential candidates have to show their understanding of SQL Injection attack methods and injection detection mechanisms to identify SQL injection attempts as well as the countermeasures.
Hacking Wireless Networks: This topic requires the knowledge of wireless encryption, Wi-Fi security tools, wireless hacking tools, and wireless hacking methodology.
Hacking Mobile Platform: This subject area evaluates the information on mobile platform attack vectors, mobile security tools and guidelines, and Android vulnerability exploitation.
Evading IDS, Honeypots, and Firewalls: For this objective, the applicants need to develop competency in Firewall, Honeypot, and IDS evasion techniques. They also need to have an understanding of techniques and tools utilized for auditing network perimeters for weaknesses & countermeasures.
Cloud Computing: This section requires the individuals’ ability to explain Cloud computing concepts, including server-less computing and Container technologies, security tools & techniques, as well as various threats and attacks. They should also have competence in penetration testing, vulnerability assessment, penetration testing roadmap, and security audit.
IoT & OT Hacking: In the framework of this module, it is important to understand threats to OT and IoT platforms, and how to securely defend IoT & OT devices.
Cryptography: The test takers need the knowledge of cryptography ciphers, cryptography attacks, crypto-analysis tools, and Public Key Infrastructure to answer the questions associated with this topic.
No Help, Full Refund
We promise you full refund if you failed 312-50v11 exam tests with our dumps. Or you can choose to wait the updating or free change to other dumps if you have other test.
Instant Download 312-50v11 Free Dumps: Upon successful payment, Our systems will automatically send the product you have purchased to your mailbox by email. (If not received within 12 hours, please contact us. Note: don't forget to check your spam.)
One-year free updating
Once you make payment for our 312-50v11 pdf, you will have access to the free update your 312-50v11 valid vce one-year. If there are latest versions released, we will send it to your email immediately. You just need to check your mailbox.
EC-COUNCIL 312-50v11 Exam Syllabus Topics:
| Section | Objectives |
|---|---|
| Topic 1: Wireless and Mobile Security | - Wireless network attacks and defenses - Mobile platform security |
| Topic 2: System Hacking and Malware Threats | - Malware analysis and countermeasures - Password cracking and privilege escalation |
| Topic 3: Scanning and Enumeration | - Enumeration techniques - Network scanning and mapping |
| Topic 4: Background and Security Fundamentals | - Ethical hacking concepts and methodologies - Information security fundamentals |
| Topic 5: Cloud, IoT, and Cryptography | - IoT security concepts - Cloud computing security - Cryptography fundamentals |
| Topic 6: Reconnaissance and Footprinting | - Footprinting and information gathering - OSINT techniques |
| Topic 7: Network and Application Attacks | - Sniffing and network attacks - Web application attacks (including SQL injection) |
| Topic 8: Defense and Countermeasures | - IDS/IPS evasion techniques - Security controls and mitigation strategies |